Independent AI execution governance

Move AI agents
from pilot to
governed production.

Assess agents before release. In production, govern model access, MCP tool calls and agent actions with policy enforcement, human approvals and compliance evidence across supported integrations.

Request a briefing
  • Starts with read-only discovery
  • Hosted SaaS, your cloud or data center
  • Deterministic policy, evaluated beside the agent

Illustrative workflow: an unsafe action is denied on a governed path. Authority is rechecked; human review and any separately permitted action are recorded separately from dispatch.

Write policy once. Enforce it everywhere.

Native controls where a platform has them. Ours where it doesn’t.

See what each surface can carry out

Governance across models, tools and actions

MCP and tools

Review MCP servers, inspect tool-call arguments, and authorize invocations.

Explore MCP governance

Agent actions

Allow, deny or hold refunds, data transfers and production changes for authorized review.

Explore action governance

Available controls depend on the integration and enforcement path.

Let AI agents act.
Hold the actions that need a human.

Identity, security and tool permission can all pass an action. GovernorAI decides whether this one should proceed.
Inside GovernorAIRecorded demo tenant
GovernorAI
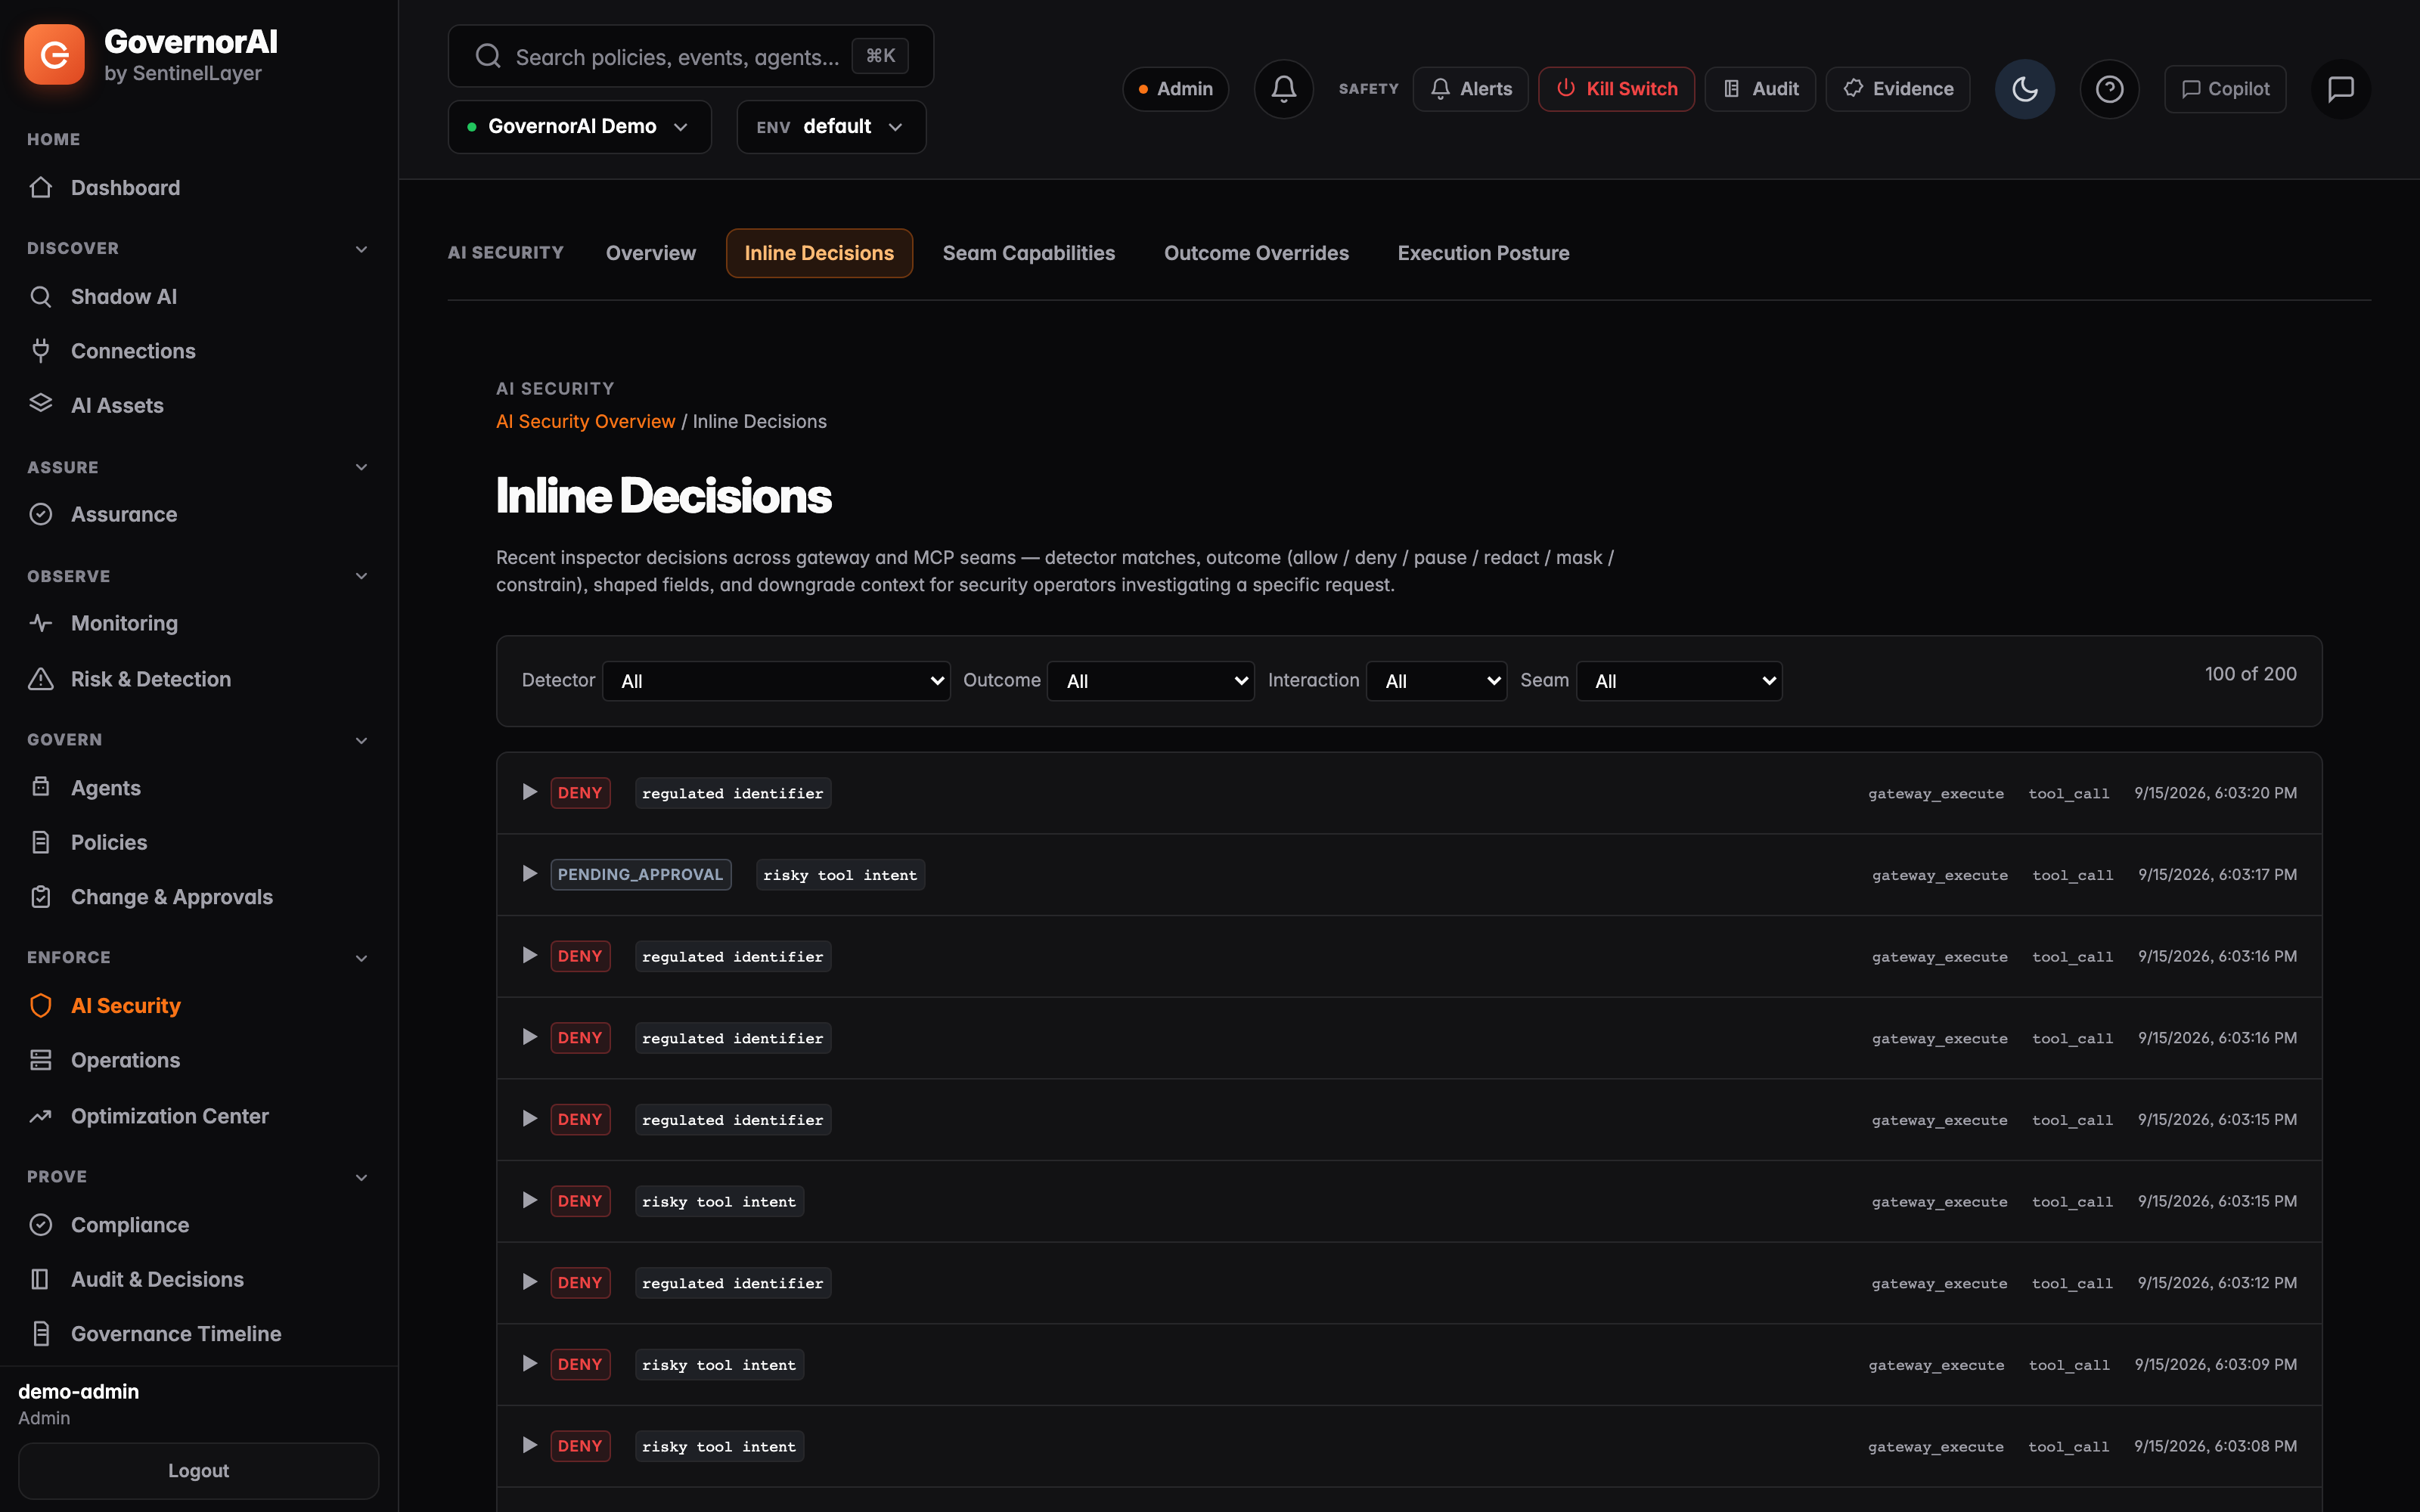
The governance lifecycle, in the product.
Published GovernorAI console screenshot showing inline allow, deny and pending-approval decisions.
Console preview. The video plays on request.
Recorded against a demo tenant with seeded activity.Recording details

Assurance earns production.
Enforcement governs it.

An agent version is assessed against the policy it will run under before it ships. Once it is live, that same policy decides each consequential action. See assurance

One governance layer
across your AI stack.

One policy model and one evidence schema at every supported enforcement point. Each integration states what it can enforce.

  • Your policyKeep your Rego and OPA review process, or write native rules.
  • Your enforcement pathsSidecars, MCP proxies, SDKs and in-tenant SaaS controls. No single provider’s gateway.
  • Your evidenceGateway records name the policy that decided them.

The refund rule, enforced in three places

Any framework, calling tools over MCPMCP proxyAllow, deny, or hold for approval
An agent on AWS BedrockBedrock inbound pathAllow, deny, or hold for approval
A write in ServiceNowBefore-write rule, before the record commitsAllow or deny. No hold on this path, so this policy denies the write.

All three share one evidence schema and one policy.

Illustrative workflow: an unsafe action is denied on a governed path. Authority is rechecked; human review and any separately permitted action are recorded separately from dispatch.

Capabilities differ by surface, and event-based controls are not inline.

View capability matrix

Govern centrally.
Enforce locally.

Agents chain dozens of tool calls, so governance overhead compounds. GovernorAI evaluates policy in a sidecar beside each agent: the policy files mounted with it, plus a Rego and kill-switch bundle the control plane signs.

When policy changes

  1. Approve
  2. Mount the files, sign the bundle
  3. Sidecar loads and pulls
  4. Verify the bundle signature
  5. Activate

When an agent acts

  1. Intercept the call
  2. Evaluate beside the agent
  3. Allow, deny or hold
  4. Record the decision
Deterministic
policy, evaluated beside the agent
Policy decides
an optional detector can only add a deny
No remote call
for routine policy decisions in sidecar mode

The gateway adapters fail closed when the gateway does not answer. Benchmark method

One policy, from the release gate to the evidence.

One versioned policy is assessed at the release gate and enforced at runtime. Gateway records name the policy that matched, when one did; they do not yet carry its revision.

assetassessed versionpolicydecisionhuman responseevidence

Decide at the action boundary.

Evaluate the action before it takes effect. Allow it, deny it, or hold it for an authorized approver where the integration supports that outcome.

Outcomes vary by enforcement point.

Explore runtime enforcement
Observability spans every stage.No fixed stage order.
“Can your evidence prove that the policy that passed your pre-production gate is the policy that made this decision?”
Today the decision record names the policy and rule that matched, not the revision, so it cannot yet answer that.

Review-ready evidence

Turn every AI decision into evidence your reviewers can trust.

GovernorAI captures the action, policy, verdict and human response as they happen—giving security and compliance teams one record they can verify, export and use in a review.

01 · Governed decisionWhat happened
Not yet verified
Current disposition

Held before dispatch.

HOLD

    Ready to verify the event sequence.

    02 · Evidence recordWhat reviewers get
    Ready to verifydecision_demo_001.json

    Decision

    Action
    support.issue_refund
    Amount
    $12,400.00
    Verdict
    HOLD
    Dispatch
    not_executed

    Policy

    Policy
    refunds
    Matched rule
    hold_high_value_refunds
    Signature
    simulated in demo

    Human

    Required role
    finance-approver
    Response
    pending

    Integrity

    Events
    3 chained
    Head hash
    —
    Status
    not yet verified

    Control mapping

    • NIST AI RMF 1.0all 72 subcategories; 13 backed by live evidencePartial
    • ISO/IEC 4200132 controls mappedPartial
    • SOC 2 · HIPAA · PCI DSS · GDPRscored from live stateAssessed
    • EU AI Act · Colorado SB 26-189programme workspaceAttestation
    Sample record, hashed in your browser. A mapping supports review; it is not a certification.Evidence & compliance →

    Make compliance part
    of execution.

    Controls, decisions and evidence come from the same system, so a review starts from records instead of reconstruction.

    1. 01

      Map requirements to controls

      Connect governance requirements to the policies and controls your teams assess.

    2. 02

      Enforce policies and approvals

      Apply policy and authorized review at supported enforcement points.

    3. 03

      Review and export evidence

      Inspect decision records, policy references and human responses for control reviews and audits.

    Mapped across eight framework packs, including SOC 2, NIST AI RMF and ISO/IEC 42001, with every control marked automatic, partial or manual attestation. Evidence supports an assessment; it does not confer certification. How evidence is produced

    Built by people who have
    operated at enterprise scale.

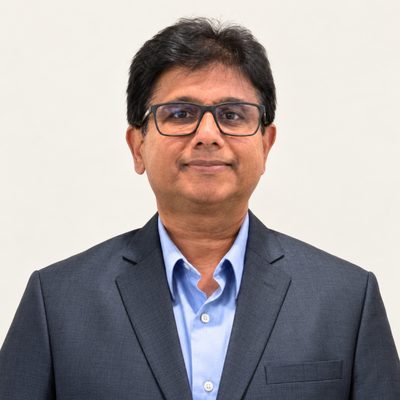
    Mynul Hoda, Founder, CEO & CTO

    Former President of Software & Platform Engineering at Viasat (850+ engineers) and its Executive Sponsor for AI Governance. Dual CCIE (Security), CISSP, Cisco Press author.

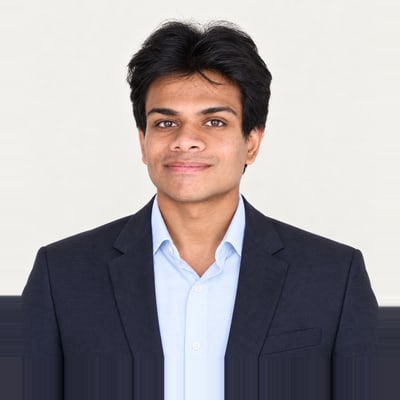
    Rayaadh Hoda, Co-founder & VP of Engineering

    Leads platform engineering, SDKs and developer experience, runtime systems and integrations.

    Earlier leadership rolesViasat2TMIBM Public CloudCisco
    RecognitionPatent pending: 2 U.S. provisional applications, 66 claimsNVIDIA Inception member

    Bring one workflow.
    Leave with a plan.

    In 30 minutes we’ll map the workflow, check integration fit and agree whether a six-week evaluation makes sense.

    Request a briefing

    We reply within 48 hours.

    Design-partner terms

    Engagement
    Six weeksAgreed controls targeted by day 30, subject to integration readiness and your approval; decision at week six
    Before day one
    Security review and accessThe six weeks start after both
    Scope
    One workflow
    Pilot license
    Waived for the agreed design-partner scope
    Your infrastructure
    Customer-funded

    Production is priced separately.

    Inspect the evidence export

    Sample data

    This is the original log for the current decision. Each event’s canonical field is the exact string that was hashed; recompute SHA-256 over it to check the hash and the link to the previous event.

    What the evidence can support

    Governance records can contribute to a control review. A framework mapping is not a certification, a completed audit or proof that every requirement is satisfied.

    Product-generated evidence

    The governed action

    Decision context, applied controls and approval history can support a review where those capabilities are configured.

    Human judgment

    The wider requirement

    Organizational procedures, management commitments and other evidence still need accountable owners and human assessment.

    Each NIST AI RMF category and ISO/IEC 42001 clause is classified as automatic, partial or manual attestation. Partial and manual items are never presented as automatically covered. The classifications are GovernorAI’s own, not independent audit findings. GovernorAI does not claim automatic certification or signed evidence by default.
    Read evidence and coverage details

    The design partner engagement

    One workflow in six weeks

    Define success before starting.

    Week one: read-only discovery and the policy for one workflow. Weeks two and three: the policy runs in shadow against live traffic and blocks nothing. Target day 30: agreed controls enabled, subject to integration readiness, test results and your approval. Week six: results against the success criteria you set on day one.

    Your team

    One accountable owner

    Bring a real workflow, the relevant platform or security lead, and a clear business constraint to evaluate.

    Our team

    Direct founder access

    Work with the people building GovernorAI. Agree on a bounded deployment and named success criteria.

    Pilot license fee waived. You cover infrastructure costs. Production is priced separately.

    Security review and read-only access happen before day one, so the six weeks are all work. Infrastructure is sized before committing. The pilot does not oblige you to continue. A named case study or logo permission is discussed only after the result and with your agreement.

    Request a briefingWe reply within 48 hours to discuss scope and fit.

    The people behind GovernorAI

    SentinelLayer brings enterprise engineering experience and hands-on platform development to the problem of governing agent actions.

    Founder, CEO & CTO

    Mynul Hoda

    Previously President of Software & Platform Engineering at Viasat, leading an 850-person organization and serving as Executive Sponsor for AI Governance. Earlier leadership roles included 2TM / Mercado Bitcoin, IBM Public Cloud and Cisco.

    Co-Founder & VP of Engineering

    Rayaadh Hoda

    Leads platform engineering and SDK development at SentinelLayer, connecting policy logic, runtime enforcement and developer experience.

    Prior employers are listed as experience, not as customers.
    Read the company profiles